Close Menu
    What's Hot

    TSMC Confirms Employee Data Leak After Hackers Claim 46,000 Records Stolen

    November 13, 2026

    Is Microsoft Outlook Hacked? Hackers Exploit Zero-Day to Steal Windows Authentication Hashes

    November 13, 2026

    PM Modi Warns of Cyber Terrorism: India’s Banking System Is a Target in Modern Economic Warfare

    November 12, 2026

    Nvidia CEO Chinese Spy Allegations: What We Know

    November 10, 2026

    Binance Hack: $6.3 Billion Crypto Theft Sparks Global Security Probe

    October 30, 2026
    Facebook X (Twitter) Instagram
    Friday, November 13
    CyberNexora News
    X (Twitter) Instagram LinkedIn
    • Home
    • Cyber Incidents
    • laws & government
    • Penalties
    • Learn & Protect
    • Resources
    • Contact Us
    Get Cyber Alerts
    CyberNexora News
    Home»Cyber Incidents»Moltbot AI Tool Draws Attention Over Security and Privacy Concerns

    Moltbot AI Tool Draws Attention Over Security and Privacy Concerns

    Zeel_CyberexpertBy Zeel_CyberexpertJanuary 29, 2026Updated:March 4, 20262 Mins Read
    Facebook Twitter LinkedIn Email Telegram

    Moltbot is a personal AI assistant tool that has recently gained attention across developer and cybersecurity communities due to concerns around how it is being deployed and used. The tool is designed to run locally or on self-hosted environments and offers automation features such as task execution, coding assistance, integrations with external services, and interaction through chat-based commands.

    The rising popularity of Moltbot has led to a large number of installations on personal systems, servers, and cloud instances. However, security professionals have observed that many deployments are being exposed to the internet without adequate access controls. In such cases, Moltbot instances can become accessible to unauthorized users, potentially exposing internal configurations, stored credentials, API keys, and interaction logs.

    The core concern is not that Moltbot itself is intentionally malicious, but that it provides powerful system-level capabilities that can pose risks if deployed without proper security measures. When misconfigured, the tool may allow external access to dashboards, command interfaces, or connected services, increasing the risk of data exposure or unintended command execution.
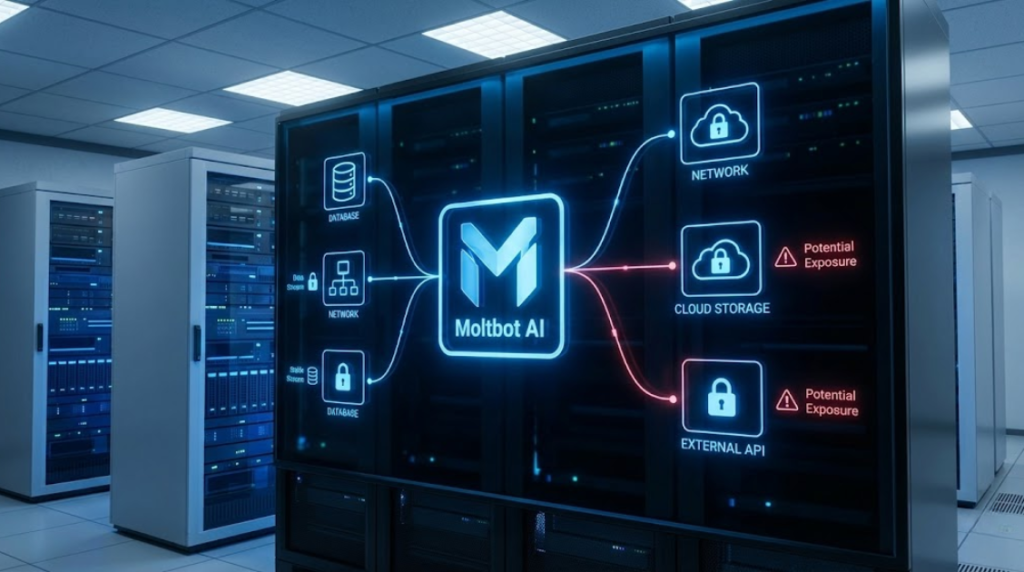
    Another area of concern involves prompt manipulation and misuse. Because Moltbot is designed to act autonomously based on user instructions, poorly designed prompts or untrusted inputs can lead to unintended actions, including disclosure of sensitive information or execution of unsafe operations. This highlights broader risks associated with autonomous AI agents when used without strict operational boundaries.

    Cybersecurity experts have emphasized that tools like Moltbot should only be deployed in controlled environments. Recommended safeguards include strong authentication, network isolation, limited permissions, careful handling of API keys, and continuous monitoring. Running such AI agents on systems that contain sensitive or production data without proper controls significantly increases security exposure.
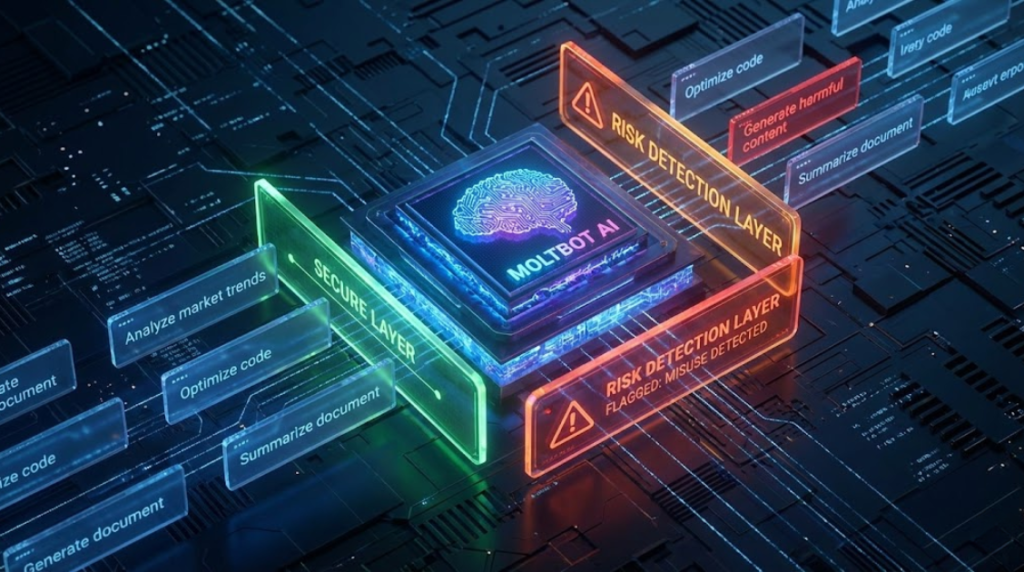
    The Moltbot discussion reflects a growing trend in which personal and enterprise AI agents are becoming more capable while also expanding the attack surface. As organizations and individuals experiment with automation-driven AI tools, security considerations are increasingly becoming as important as functionality.

    While Moltbot continues to gain traction for its flexibility and automation potential, professionals caution that responsible deployment and security-first configuration are essential to prevent misuse or accidental data exposure. The situation serves as a reminder that emerging AI tools must be treated with the same security discipline as any other system with access to sensitive resources.

    Related Articles

  • LLM-Generated Mythic Agents: AI Creates Disposable Malware Introduction: LLM-Generated Mythic Agents — Why It Matters The rise...
  • AutoJack Exploit Hijacks Microsoft AI Agent via Web Page Introduction: AutoJack Exploit — Why It Matters The AutoJack Exploit...
  • Mistic Backdoor Linked to KongTuke Targets Organizations via ClickFix Introduction: Why the Mistic Backdoor Matters A newly discovered stealth...
  • Google Vertex AI Default Setup Lets Low-Privileged Users Hijack Service Agent Access Security researchers have reported a security risk in Google Vertex...
  • Five Eyes AI Cyber Threat Warning: Frontier Model Risks Introduction: Five Eyes AI Cyber Threat Warning — Why It...
  • Share. Facebook Twitter LinkedIn Email Telegram

    latest news

    TSMC Confirms Employee Data Leak After Hackers Claim 46,000 Records Stolen

    November 13, 2026

    Is Microsoft Outlook Hacked? Hackers Exploit Zero-Day to Steal Windows Authentication Hashes

    November 13, 2026

    PM Modi Warns of Cyber Terrorism: India’s Banking System Is a Target in Modern Economic Warfare

    November 12, 2026

    Nvidia CEO Chinese Spy Allegations: What We Know

    November 10, 2026

    Binance Hack: $6.3 Billion Crypto Theft Sparks Global Security Probe

    October 30, 2026

    Black October 2026: The Global Cybersecurity Wake-Up Call

    October 24, 2026

    VAPT Services in 2026: Why Vulnerability Assessment and Penetration Testing Are Essential for Cybersecurity

    October 22, 2026

    SBI Data Breach: 3.75 Lakh Dark Web Records Reviewed

    October 21, 2026

    AI Reverse Engineering Goes Viral as Adobe and Microsoft Face New Software Competition

    October 19, 2026

    Denmark Data Breach: 8.8 Million Records Accessed

    October 17, 2026
    Recent Posts
    • TSMC Confirms Employee Data Leak After Hackers Claim 46,000 Records Stolen
    • Is Microsoft Outlook Hacked? Hackers Exploit Zero-Day to Steal Windows Authentication Hashes
    • PM Modi Warns of Cyber Terrorism: India’s Banking System Is a Target in Modern Economic Warfare
    Top Posts

    Unauthorized Access Incident at Coupang Exposes Customer Data

    December 29, 2025

    TSMC Confirms Employee Data Leak After Hackers Claim 46,000 Records Stolen

    November 13, 2026

    Significant Data Breach at Korean Air Subcontractor Exposes Employee Records

    December 29, 2025
    About

    CyberNexora Blog provides trusted cybersecurity news, attack analysis, and security awareness updates. Our goal is to educate and inform readers about emerging cyber threats and best protection practices.

    Facebook X (Twitter) Instagram Pinterest LinkedIn
    Pages
    • Home
    • Cyber Incidents
    • laws & government
    • Penalties
    • Learn & Protect
    • Resources
    • Contact Us

    Get Cyber Security Alerts

    Thanks! Please check your email to confirm subscription.

    • About CyberNexora News
    • Privacy Policy
    © 2026 CyberNexora News. All Rights Reserved.

    Type above and press Enter to search. Press Esc to cancel.