Close Menu
    What's Hot

    TSMC Confirms Employee Data Leak After Hackers Claim 46,000 Records Stolen

    November 13, 2026

    Is Microsoft Outlook Hacked? Hackers Exploit Zero-Day to Steal Windows Authentication Hashes

    November 13, 2026

    PM Modi Warns of Cyber Terrorism: India’s Banking System Is a Target in Modern Economic Warfare

    November 12, 2026

    Nvidia CEO Chinese Spy Allegations: What We Know

    November 10, 2026

    Binance Hack: $6.3 Billion Crypto Theft Sparks Global Security Probe

    October 30, 2026
    Facebook X (Twitter) Instagram
    Friday, November 13
    CyberNexora News
    X (Twitter) Instagram LinkedIn
    • Home
    • Cyber Incidents
    • laws & government
    • Penalties
    • Learn & Protect
    • Resources
    • Contact Us
    Get Cyber Alerts
    CyberNexora News
    Home»Cyber Incidents»Google Vertex AI Default Setup Lets Low-Privileged Users Hijack Service Agent Access

    Google Vertex AI Default Setup Lets Low-Privileged Users Hijack Service Agent Access

    Privilege Escalation Risk Identified in Default Configuration of Google Vertex AI
    Zeel_CyberexpertBy Zeel_CyberexpertJanuary 18, 2026Updated:March 4, 20262 Mins Read
    Facebook Twitter LinkedIn Email Telegram

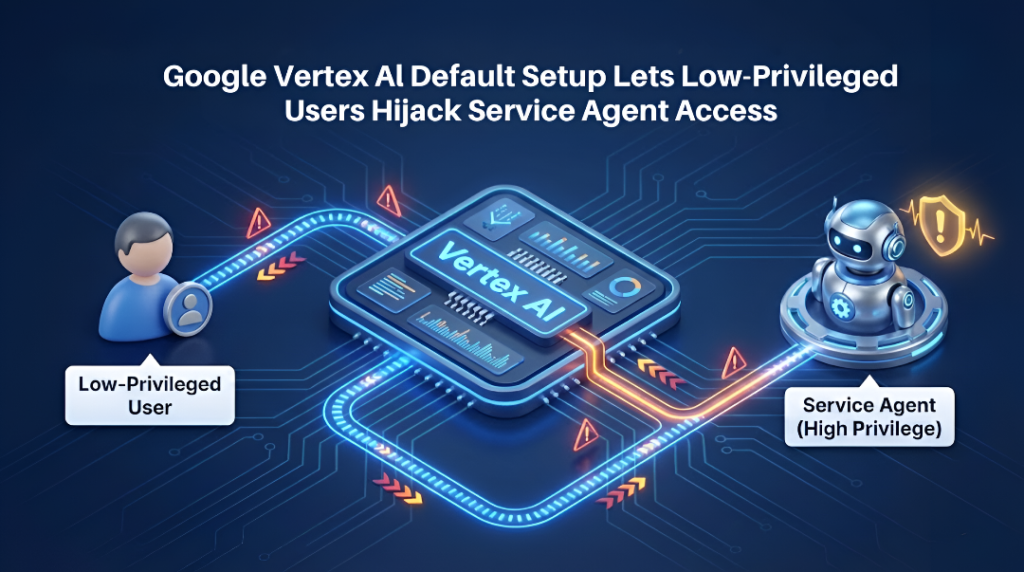
    Security researchers have reported a security risk in Google Vertex AI related to its default configuration. The issue allows users with low or read-level permissions to indirectly obtain high-privilege Service Agent access, which can impact enterprise cloud environments.

    The findings were disclosed by XM Cyber researchers and later reviewed by Google, which stated that the behavior aligns with the current design model. Researchers, however, demonstrated that this design can lead to real-world privilege escalation scenarios.

    Overview of the Issue

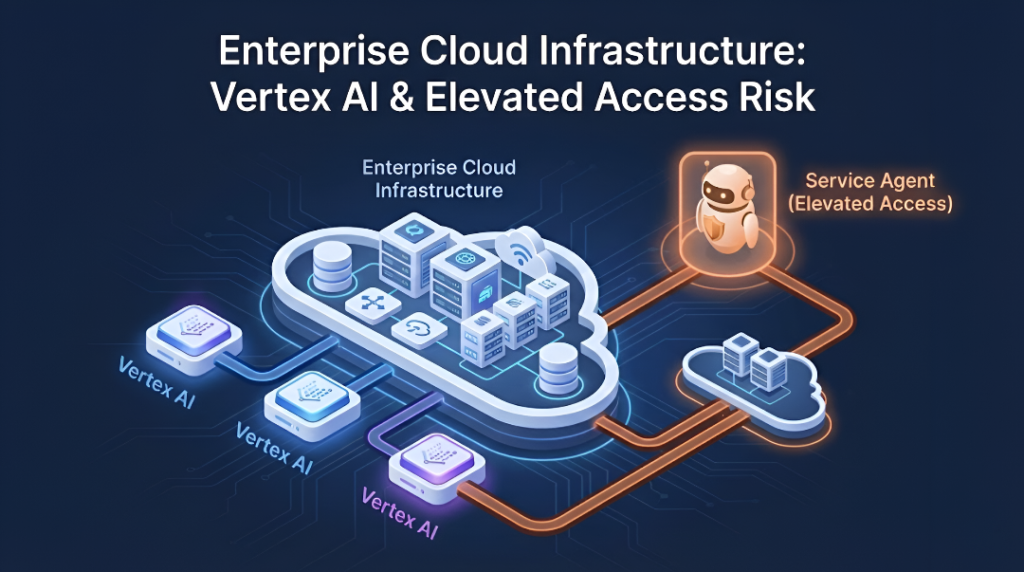
    Vertex AI uses Service Agents, which are Google-managed identities attached automatically to AI components for internal operations.
    These Service Agents are granted broad project-level permissions by default.

    Researchers observed that when access to these Service Agents is indirectly exposed, users with limited permissions may be able to perform actions beyond their assigned role, without modifying IAM policies.
    Affected Vertex AI Components

    The risk was confirmed in two Vertex AI components:

    • Vertex AI Agent Engine
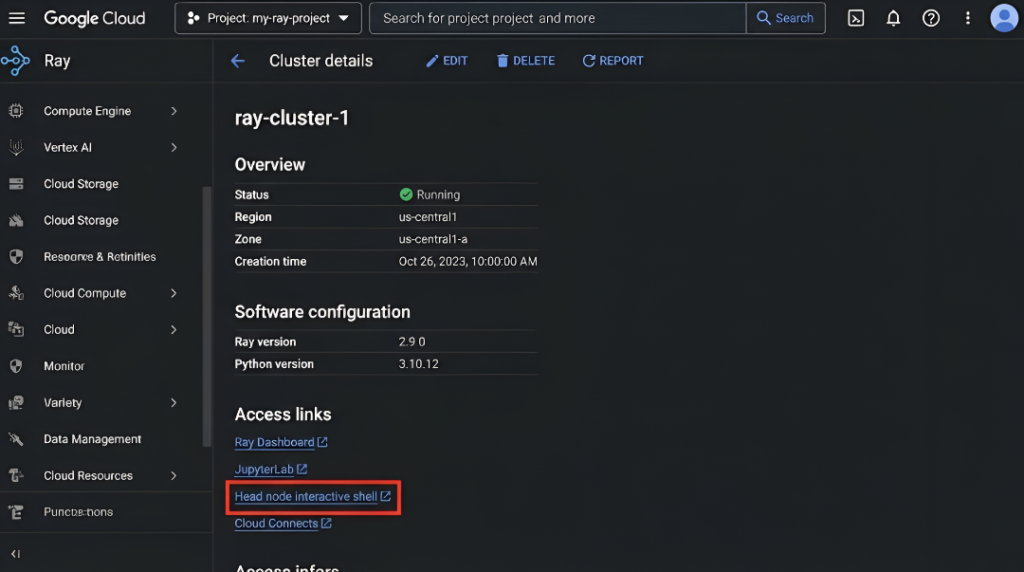
    • Ray on Vertex AI

    In both cases, the issue is linked to permission inheritance and default trust relationships, not to malware, zero-day exploits, or software bugs.

    Observed Impact (Validated)
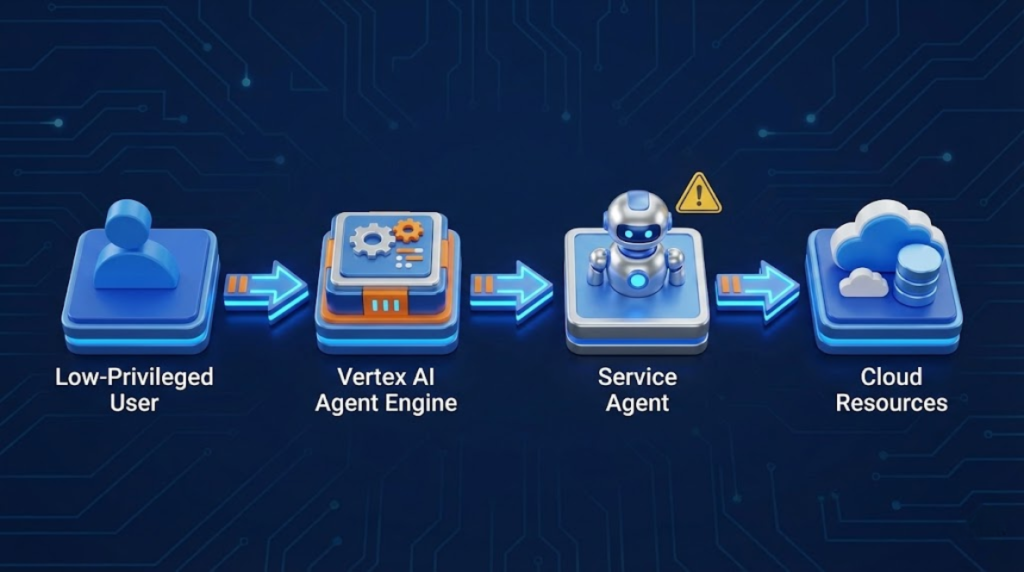
    According to XM Cyber’s analysis, the default behavior can result in:

    • Access to AI agent memory and session data
    • Visibility into logging and operational data
    • Read and write access to Cloud Storage resources
    • Read and write access to BigQuery datasets (in Ray-based environments)

    These outcomes were observed starting from read-level permissions, making the escalation risk significant for enterprise deployments.

    Summary of Findings

    ComponentService Agent InvolvedInitial Access LevelObserved Risk
    Vertex AI Agent EngineReasoning Engine Service AgentLimited update accessExposure of AI data and storage
    Ray on Vertex AICustom Code Service AgentViewer-level accessElevated access to storage and analytics

    Why This Matters

    Vertex AI is widely used for production AI workloads, where systems often process sensitive business data.
    When Service Agents hold extensive permissions by default, any indirect exposure increases the attack surface and expands the potential impact across a cloud project.

    Security researchers describe this as a confused-deputy risk, where trusted system components unintentionally perform actions on behalf of low-privileged users.
    Current Status

    • The issue was responsibly disclosed to Google
    • Google reviewed the findings and classified them as design-related
    • No changes to default Service Agent permissions have been announced
    • Researchers advise enterprises to treat default Vertex AI configurations as risk-bearing, not secure baselines

    Related Articles

  • AutoJack Exploit Hijacks Microsoft AI Agent via Web Page Introduction: AutoJack Exploit — Why It Matters The AutoJack Exploit...
  • Cloud Security 2026: Why It’s the Most Critical Cybersecurity Skill Today and for the Future Over the last few years, the technology landscape has changed...
  • Google AI-Generated Zero-Day Exploit 2026: Cybersecurity Enters a New Era of AI-Powered Attacks Introduction: Google AI-Generated Zero-Day Exploit Raises Global Cybersecurity Concerns The...
  • Five Eyes AI Cyber Threat Warning: Frontier Model Risks Introduction: Five Eyes AI Cyber Threat Warning — Why It...
  • Google Disrupts Sophisticated Chinese Cyber Espionage Operation Targeting Governments and Telecom Networks Google’s Threat Intelligence Group (GTIG), in collaboration with Mandiant and...
  • Share. Facebook Twitter LinkedIn Email Telegram

    latest news

    TSMC Confirms Employee Data Leak After Hackers Claim 46,000 Records Stolen

    November 13, 2026

    Is Microsoft Outlook Hacked? Hackers Exploit Zero-Day to Steal Windows Authentication Hashes

    November 13, 2026

    PM Modi Warns of Cyber Terrorism: India’s Banking System Is a Target in Modern Economic Warfare

    November 12, 2026

    Nvidia CEO Chinese Spy Allegations: What We Know

    November 10, 2026

    Binance Hack: $6.3 Billion Crypto Theft Sparks Global Security Probe

    October 30, 2026

    Black October 2026: The Global Cybersecurity Wake-Up Call

    October 24, 2026

    VAPT Services in 2026: Why Vulnerability Assessment and Penetration Testing Are Essential for Cybersecurity

    October 22, 2026

    SBI Data Breach: 3.75 Lakh Dark Web Records Reviewed

    October 21, 2026

    AI Reverse Engineering Goes Viral as Adobe and Microsoft Face New Software Competition

    October 19, 2026

    Denmark Data Breach: 8.8 Million Records Accessed

    October 17, 2026
    Recent Posts
    • TSMC Confirms Employee Data Leak After Hackers Claim 46,000 Records Stolen
    • Is Microsoft Outlook Hacked? Hackers Exploit Zero-Day to Steal Windows Authentication Hashes
    • PM Modi Warns of Cyber Terrorism: India’s Banking System Is a Target in Modern Economic Warfare
    Top Posts

    Unauthorized Access Incident at Coupang Exposes Customer Data

    December 29, 2025

    TSMC Confirms Employee Data Leak After Hackers Claim 46,000 Records Stolen

    November 13, 2026

    Significant Data Breach at Korean Air Subcontractor Exposes Employee Records

    December 29, 2025
    About

    CyberNexora Blog provides trusted cybersecurity news, attack analysis, and security awareness updates. Our goal is to educate and inform readers about emerging cyber threats and best protection practices.

    Facebook X (Twitter) Instagram Pinterest LinkedIn
    Pages
    • Home
    • Cyber Incidents
    • laws & government
    • Penalties
    • Learn & Protect
    • Resources
    • Contact Us

    Get Cyber Security Alerts

    Thanks! Please check your email to confirm subscription.

    • About CyberNexora News
    • Privacy Policy
    © 2026 CyberNexora News. All Rights Reserved.

    Type above and press Enter to search. Press Esc to cancel.