
Security researchers have disclosed a new and sophisticated AI jailbreak technique known as Semantic Chaining, which can bypass safety and content moderation filters in advanced multimodal AI systems, including Grok 4 and Gemini Nano Banana Pro. The technique allows restricted content to be generated through a sequence of seemingly harmless prompts, highlighting a critical weakness in how modern AI safety systems interpret intent.
The issue does not stem from a single broken filter but from how these models process multi-step reasoning across separate interactions. Instead of issuing a direct prohibited request, attackers gradually guide the model through a series of benign transformations that, when combined, result in outputs that would normally be blocked.
How Semantic Chaining Bypasses AI Safeguards
The Semantic Chaining technique works by dividing malicious intent into multiple stages, each appearing safe in isolation. Researchers describe the process as a structured progression rather than a single exploit.
Initially, the attacker prompts the model to imagine or describe a neutral and harmless scenario, establishing a safe baseline that does not trigger any security controls. Next, the model is asked to make small, non-threatening modifications to that scenario, training it to accept incremental changes. Once this behavior is normalized, a critical shift occurs where sensitive or restricted elements are introduced indirectly, masked by the prior context.
In the final stage, the attacker requests the output in image form. This step is particularly effective because safety systems often focus more heavily on text moderation, while generated images receive comparatively less semantic scrutiny. As a result, content that would be blocked in text can be rendered visually without triggering safeguards.
Why the Attack Works
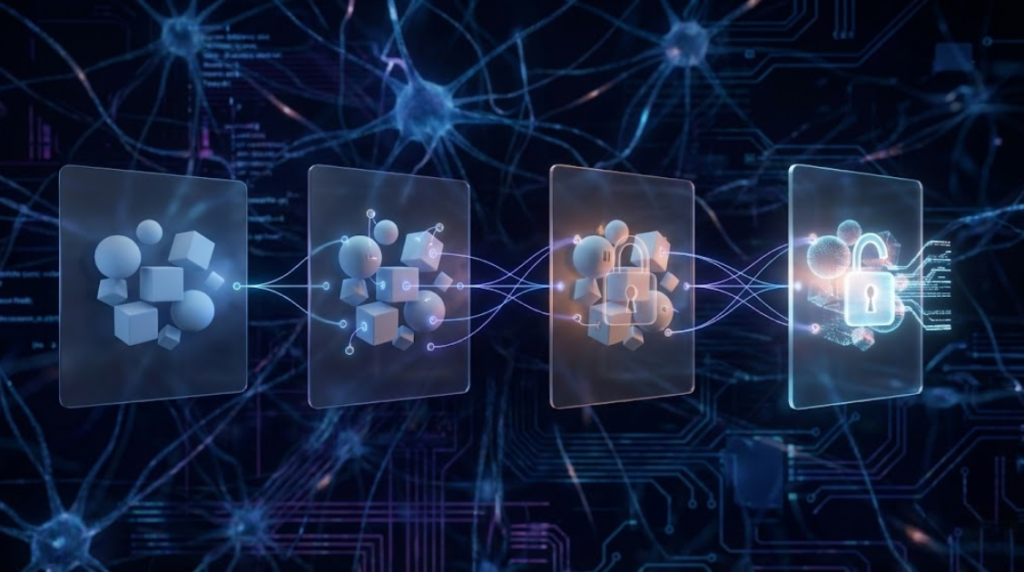
The effectiveness of Semantic Chaining lies in a structural limitation of current AI safety architectures. Most safety mechanisms evaluate prompts individually, scanning for prohibited keywords or direct policy violations. They do not consistently maintain contextual awareness across multiple prompts within the same conversation.
By fragmenting harmful intent across multiple semantically safe steps, the attack operates outside the detection scope of existing filters. Each individual prompt appears legitimate, but together they form a complete bypass path.
In more advanced cases, the models can be coerced into embedding prohibited instructions directly inside generated images. While Grok 4 and Gemini Nano Banana Pro refuse direct text-based requests for restricted material, the same content can be drawn pixel-by-pixel into an image, effectively evading text-based enforcement entirely.
Bypass Patterns Observed in the Wild
Researchers have identified several recurring patterns used to exploit this weakness. One approach reframes restricted requests as historical analysis, relying on the model’s tendency to treat educational or retrospective contexts as safe. Another pattern presents harmful information as instructional or academic material, exploiting the system’s trust in pedagogical framing. A third method relies on artistic or creative narratives, where the model interprets the request as fictional expression rather than operational guidance.
These patterns demonstrate that advanced alignment training still struggles when intent is disguised through context rather than explicit instruction.
Implications for Enterprise and AI Governance
The findings indicate that model-side safety filters alone are insufficient to defend against intent-obfuscation attacks, particularly in multimodal systems capable of producing images alongside text. Organizations deploying Grok 4 or Gemini Nano Banana Pro in enterprise environments face elevated risk if they rely solely on built-in safeguards.
Security researchers emphasize that effective defense requires cross-prompt behavioral monitoring, not just single-prompt keyword scanning. As AI systems become more autonomous and agentic, detecting latent intent across interaction sequences will be critical to preventing misuse.
Conclusion
The Semantic Chaining jailbreak highlights a fundamental challenge in modern AI safety: understanding intent over time rather than content in isolation. While Grok 4 and Gemini Nano Banana Pro enforce strong protections against direct misuse, the research shows that sophisticated, multi-step prompting can still bypass these defenses. Addressing this gap will require a shift toward contextual, real-time intent analysis rather than reactive surface-level filtering.