Close Menu
    What's Hot

    Viral “Rent A Garba Partner” Post Raises Cybersecurity Questions Amid Navratri Scam Warnings

    September 19, 2026

    Azure AI Foundry Vulnerability: CVSS 10.0

    September 18, 2026

    T-Mobile Rewards Phishing: Fake Expiry Scam Texts

    September 18, 2026

    Docker Sandboxes Vulnerabilities: Critical Flaws

    September 17, 2026

    HEAVYGRAM Malware: Telegram Surveillance Backdoor

    September 17, 2026
    Facebook X (Twitter) Instagram
    Monday, September 21
    CyberNexora News
    X (Twitter) Instagram LinkedIn
    • Home
    • Cyber Incidents
    • laws & government
    • Penalties
    • Learn & Protect
    • Resources
    • Contact Us
    Get Cyber Alerts
    CyberNexora News
    Home»Cyber Incidents»Hackers Are Wiping Exposed MongoDB Databases and Leaving Ransom Notes

    Hackers Are Wiping Exposed MongoDB Databases and Leaving Ransom Notes

    Zeel_CyberexpertBy Zeel_CyberexpertFebruary 2, 2026Updated:March 4, 20262 Mins Read
    Facebook Twitter LinkedIn Email Telegram

    Cybersecurity researchers are warning about an ongoing wave of attacks targeting exposed MongoDB database instances on the internet. In these attacks, hackers are not stealing data — instead, they are completely deleting databases and replacing them with ransom notes demanding payment.

    The attacks mainly affect MongoDB servers that are misconfigured and accessible without authentication. Attackers use automated scanning tools to find such databases, gain access within seconds, erase all collections, and then create a new database containing a ransom message. Victims are asked to pay a small amount in cryptocurrency in exchange for a claimed data recovery solution.

    Security experts have made it clear that paying the ransom does not guarantee data recovery. In many reported cases, the deleted data could not be restored even after payment, as attackers often do not possess any real backups. The attack works more like data destruction combined with extortion, rather than traditional ransomware.
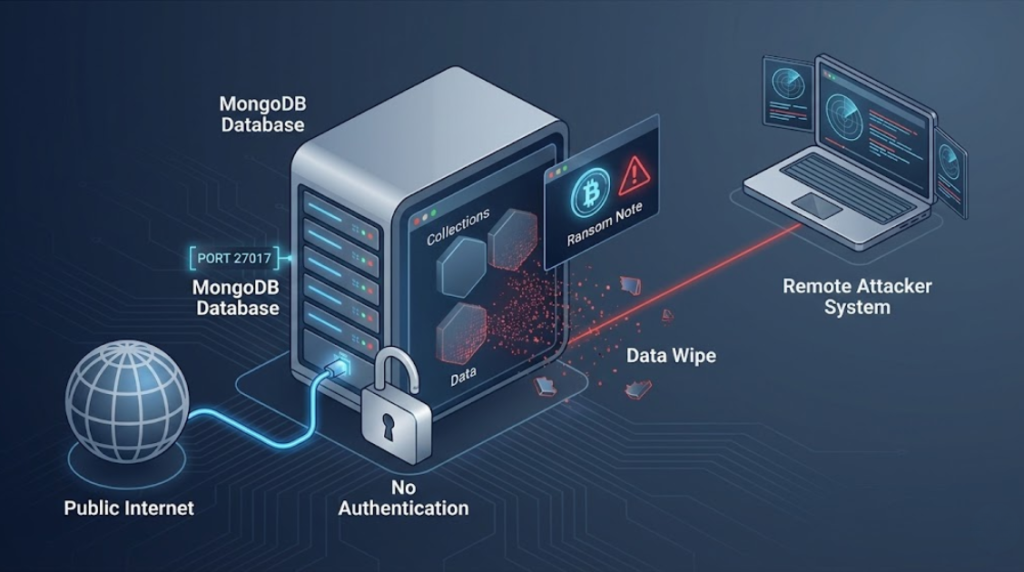
    Researchers have observed that thousands of MongoDB instances remain publicly exposed, often due to default configurations, lack of firewall rules, or databases being directly accessible from the internet. These attacks do not rely on advanced vulnerabilities or zero-day exploits — they succeed mainly because of basic security misconfigurations.

    Administrators are strongly advised to restrict public access to MongoDB, enable authentication, use network firewalls, and ensure regular backups are in place. Experts emphasize that properly configured MongoDB servers are not affected by this campaign.

    This incident is a reminder that even simple configuration mistakes can lead to serious data loss. Organizations and developers using MongoDB must treat database exposure as a critical risk, not a minor oversight.

    Related Articles

  • How to Recover a Hacked Instagram Account — India’s Complete Step-by-Step Guide Introduction: How to Recover a Hacked Instagram Account — Why...
  • Signal Backup Recovery Key Phishing: Critical FBI Warning Introduction: Signal Backup Recovery Key Phishing — Why It Matters...
  • Ransomware-as-a-Service: How Criminals Scale Cyberattacks Introduction: Ransomware-as-a-Service — Why It Matters Ransomware-as-a-Service has transformed ransomware...
  • Oracle E-Business Suite Flaw CVE-2026-46817 Under Active Attack Oracle E-Business Suite Flaw CVE-2026-46817 — Why It Matters Security...
  • Kairos Data-Theft Extortion: $1M Government Payment Introduction: Kairos Data-Theft Extortion — Why It Matters The Kairos...
  • Share. Facebook Twitter LinkedIn Email Telegram

    latest news

    Viral “Rent A Garba Partner” Post Raises Cybersecurity Questions Amid Navratri Scam Warnings

    September 19, 2026

    Azure AI Foundry Vulnerability: CVSS 10.0

    September 18, 2026

    T-Mobile Rewards Phishing: Fake Expiry Scam Texts

    September 18, 2026

    Docker Sandboxes Vulnerabilities: Critical Flaws

    September 17, 2026

    HEAVYGRAM Malware: Telegram Surveillance Backdoor

    September 17, 2026

    SparroWocky Backdoor: FamousSparrow Targets Governments

    September 17, 2026

    CenterPoint Energy Data Breach: Customer Data Exposed

    September 16, 2026

    BambooToken Malware: Critical MQTT C2 Campaign

    September 16, 2026

    WordPress Plugin Attacks: Critical RCE Flaws Exposed

    September 16, 2026

    Apple Security Update: 273 Vulnerabilities Fixed

    September 16, 2026
    Recent Posts
    • Viral “Rent A Garba Partner” Post Raises Cybersecurity Questions Amid Navratri Scam Warnings
    • Azure AI Foundry Vulnerability: CVSS 10.0
    • T-Mobile Rewards Phishing: Fake Expiry Scam Texts
    Top Posts

    Viral “Rent A Garba Partner” Post Raises Cybersecurity Questions Amid Navratri Scam Warnings

    September 19, 2026

    Unauthorized Access Incident at Coupang Exposes Customer Data

    December 29, 2025

    Significant Data Breach at Korean Air Subcontractor Exposes Employee Records

    December 29, 2025
    About

    CyberNexora Blog provides trusted cybersecurity news, attack analysis, and security awareness updates. Our goal is to educate and inform readers about emerging cyber threats and best protection practices.

    Facebook X (Twitter) Instagram Pinterest LinkedIn
    Pages
    • Home
    • Cyber Incidents
    • laws & government
    • Penalties
    • Learn & Protect
    • Resources
    • Contact Us

    Get Cyber Security Alerts

    Thanks! Please check your email to confirm subscription.

    • About CyberNexora News
    • Privacy Policy
    © 2026 CyberNexora News. All Rights Reserved.

    Type above and press Enter to search. Press Esc to cancel.