
NVIDIA Faces a Ransomware Threat: What We Know So Far
Has NVIDIA been hacked? That question is drawing attention across the cybersecurity industry after a ransomware group known as The Gentlemen claimed to have compromised the global AI chipmaker.
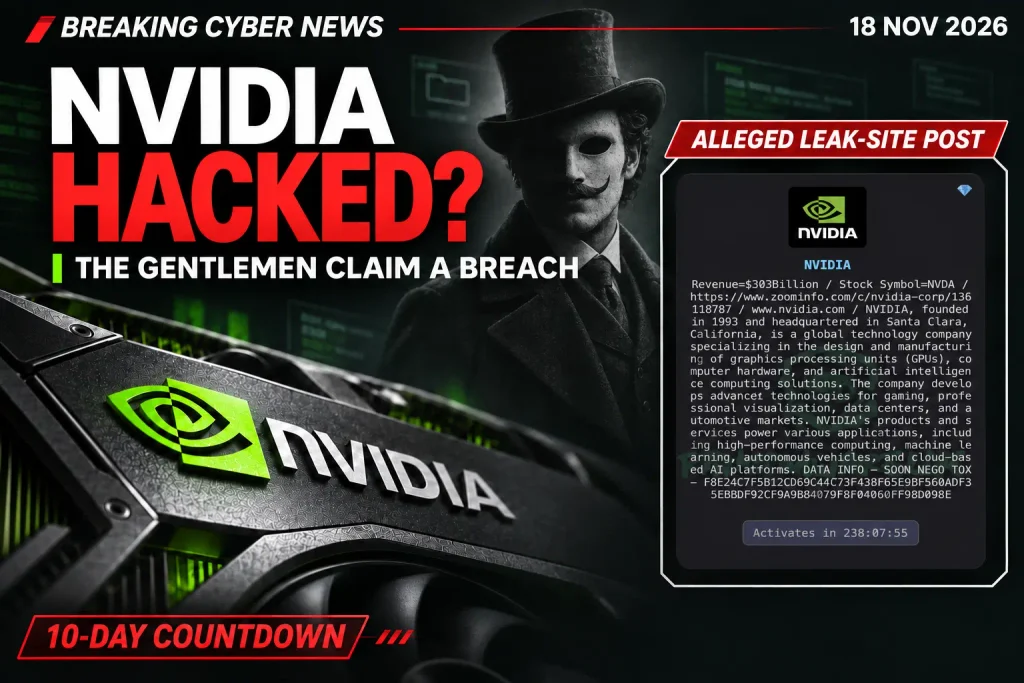
On 18 November 2026, NVIDIA appeared on the group’s dark-web extortion website alongside a countdown of approximately 10 days.
The attackers suggest that allegedly stolen information could be released when the countdown ends.
However, there is a crucial distinction between a ransomware claim and a confirmed security breach.
As of 18 November 2026, NVIDIA has not publicly confirmed a breach, and the attackers have not released verifiable evidence of stolen data.
The incident remains an unverified ransomware allegation.
Still, the development raises an important question:
If a company central to the global AI industry can become the subject of a ransomware threat, how prepared are other businesses to handle similar pressure?
What Happened in the Alleged NVIDIA Ransomware Attack?
According to cybersecurity reporting, The Gentlemen added NVIDIA to its dark-web leak site on 18 November 2026.
The listing included several notable details:
- Target named: NVIDIA Corporation, the global AI and semiconductor company.
- Threat actor: The Gentlemen ransomware group.
- Countdown: Approximately 234 hours, or just under 10 days.
- Data status: A message indicating that information about the alleged data leak would be provided later.
- Negotiation contact: A Tox messaging identifier, potentially intended for ransom discussions.
- Evidence released: No publicly verifiable stolen files or technical proof.
The countdown points toward approximately 28 November 2026, although the deadline is controlled by the attackers and could change.
At present, the listing does not establish when any intrusion might have happened, which systems may have been affected or whether confidential NVIDIA data was actually obtained.
Is NVIDIA Really Hacked?
There is currently no independent confirmation that NVIDIA’s systems have been compromised in this alleged incident.
Three important facts remain unresolved:
1. No stolen data samples
The Gentlemen has not publicly provided samples of confidential NVIDIA documents that would substantiate its claim.
2. No confirmed technical evidence
There is no publicly verified evidence demonstrating an intrusion into NVIDIA’s internal systems or the deployment of ransomware.
3. No company confirmation
NVIDIA has not publicly confirmed the alleged breach as of this article’s publication.
Cybernews has also reported that The Gentlemen has previously made exaggerated or incorrectly attributed claims.
This means the latest NVIDIA listing should be treated seriously as a threat-intelligence development, but not as proof that a successful cyberattack occurred.
Who Is The Gentlemen Ransomware Group?
The Gentlemen is an established ransomware-as-a-service (RaaS) operation that emerged in 2025.
In a RaaS model, ransomware operators maintain the malware and infrastructure while affiliates may conduct attacks against target organisations.
The group has been associated with numerous victim claims across different industries and countries.
Check Point Research has studied its operations, including internal information that became exposed during 2026.
That research provided insight into the group’s infrastructure, affiliate activity and use of AI-assisted development tools.
The Gentlemen has demonstrated considerable activity in the ransomware ecosystem.
However, a group’s history does not automatically validate every new victim claim.
Each alleged breach must be assessed using reliable technical evidence, confirmed disclosures or independently verified leaked information.
Why Is the NVIDIA Ransomware News Attracting So Much Attention?
The timing is particularly notable.
On 17 November 2026, NVIDIA officially announced revenue of $115.8 billion for the third quarter of fiscal 2027.
That represented a 103% increase compared with the same quarter a year earlier.
Just a day later, the NVIDIA ransomware allegation gained attention.
NVIDIA plays a major role in global AI computing infrastructure, including GPU technology, data-centre systems and enterprise computing.
A genuine cybersecurity incident involving such a company could potentially raise questions about:
- Protection of confidential business information.
- Employee and corporate data security.
- Intellectual property safeguards.
- Supplier and partner security.
- Business continuity and incident response.
Important: These are potential risk categories, not confirmed consequences of this alleged attack.
There is currently no verified evidence linking NVIDIA’s financial results to the ransomware group’s actions.
The timing alone does not establish a connection.
What Happens When the 10-Day Countdown Ends?
The countdown is one of the most attention-grabbing aspects of this case.
But what happens when it reaches zero?
There are three realistic possibilities.
Scenario 1: The Attackers Release Data
The Gentlemen could publish samples or files it claims belong to NVIDIA.
If that happens, cybersecurity researchers would need to verify whether the material is authentic, current and obtained through an actual compromise.
A file appearing on a leak site does not automatically prove a new breach.
Scenario 2: The Countdown Is Extended
Ransomware groups sometimes change deadlines to maintain pressure on alleged victims.
The timer could therefore continue beyond its initially displayed date.
Scenario 3: No Verifiable Evidence Appears
The listing could remain unsupported, disappear or be updated without meaningful proof.
That would leave the original hacking claim unverified.
The key event to watch is not simply the countdown reaching zero. It is whether credible evidence of a breach emerges.
Could a Confirmed NVIDIA Breach Affect Other Businesses?
If a significant breach were independently confirmed, investigators would need to establish its scope before assessing any downstream risk.
That includes identifying potentially affected systems, data categories and business relationships.
But at this stage, there is no verified basis for claiming that NVIDIA customers, AI products, GPUs or partner networks have been compromised through this alleged incident.
Businesses should avoid acting on speculation while remaining alert to verified security advisories and official communications.
The broader lesson is straightforward:
Cybersecurity incidents can create operational and reputational pressure long before the full facts become public.
That is why incident preparedness matters.
What Businesses Can Learn From the NVIDIA Ransomware Claim
Whether the reported NVIDIA breach is eventually confirmed or disproved, ransomware continues to pose a serious risk to organisations worldwide.
Businesses should focus on practical security measures.
1. Protect Critical Access
Use strong authentication, multi-factor authentication and appropriate access restrictions for privileged accounts.
2. Test Security Before Attackers Do
Conduct authorised vulnerability assessments and penetration testing across websites, applications, APIs and exposed infrastructure.
3. Maintain Secure Backups
Keep tested, appropriately isolated backups to support recovery if systems become unavailable.
4. Monitor for Suspicious Activity
Detect unusual access attempts, credential misuse, suspicious file activity and unexpected system changes.
5. Prepare an Incident Response Plan
Define responsibilities, evidence-preservation procedures, escalation processes and communication requirements before a crisis.
No organisation can guarantee that every attack will be prevented.
However, proactive security testing and effective response planning can reduce exposure and improve resilience.
FAQs About the NVIDIA Ransomware Attack
Was NVIDIA hacked in November 2026?
As of 18 November 2026, there is no independently confirmed breach associated with The Gentlemen’s latest claim. The group has listed NVIDIA on its leak site, but it has not publicly provided verifiable evidence of stolen data.
Which ransomware group claims to have hacked NVIDIA?
A ransomware group called The Gentlemen has claimed NVIDIA as a victim. The group operates within the ransomware-as-a-service ecosystem and has been the subject of cybersecurity research.
Has NVIDIA’s stolen data been leaked online?
No verified NVIDIA data samples associated with this allegation had been publicly released as of 18 November 2026. The existence and nature of any allegedly stolen information remain unconfirmed.
When will The Gentlemen release NVIDIA’s alleged data?
The gang initially displayed a countdown of approximately 234 hours on 18 November 2026, suggesting a deadline around 28 November 2026. However, the timer is controlled by the attackers and does not guarantee that any data will be published.
How much ransom has The Gentlemen demanded from NVIDIA?
No specific ransom amount has been publicly verified. The group’s listing includes an encrypted contact identifier for possible negotiations, but that does not establish whether NVIDIA received a demand or entered discussions.