Close Menu
    What's Hot

    OpenAI AI Agents Breached Australian Government Portal in Wider Hacking Campaign

    September 28, 2026

    Viral “Rent A Garba Partner” Post Raises Cybersecurity Questions Amid Navratri Scam Warnings

    September 19, 2026

    Azure AI Foundry Vulnerability: CVSS 10.0

    September 18, 2026

    T-Mobile Rewards Phishing: Fake Expiry Scam Texts

    September 18, 2026

    Docker Sandboxes Vulnerabilities: Critical Flaws

    September 17, 2026
    Facebook X (Twitter) Instagram
    Monday, September 28
    CyberNexora News
    X (Twitter) Instagram LinkedIn
    • Home
    • Cyber Incidents
    • laws & government
    • Penalties
    • Learn & Protect
    • Resources
    • Contact Us
    Get Cyber Alerts
    CyberNexora News
    Home»laws & government»DoT’s SIM-Binding Rule Comes Into Effect from March 1: What It Means for WhatsApp, Telegram and Other Messaging Apps

    DoT’s SIM-Binding Rule Comes Into Effect from March 1: What It Means for WhatsApp, Telegram and Other Messaging Apps

    Zeel_CyberexpertBy Zeel_CyberexpertMarch 1, 2026Updated:March 4, 20263 Mins Read
    Facebook Twitter LinkedIn Email Telegram

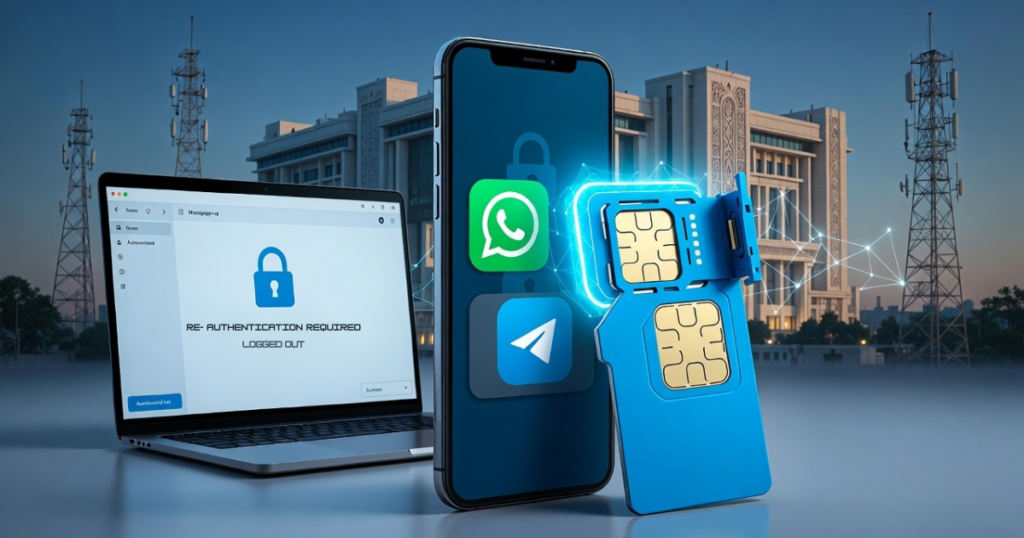
    India’s Department of Telecommunications (DoT) has enforced a new SIM-binding rule starting March 1, 2026. The directive applies to messaging platforms that use mobile numbers for user authentication, including WhatsApp, Telegram, Signal and similar apps.

    The order was originally issued on November 28, 2025, giving companies 90 days to comply.

    What Is SIM-Binding?

    Currently, most messaging apps verify users using a one-time password (OTP) sent to their registered mobile number during sign-up. After verification, the app can continue functioning even if the SIM card is removed or deactivated, particularly in multi-device and web versions.

    Under the new SIM-binding rule:

    • The messaging app must function only when the registered SIM card is present in the user’s primary mobile device.
    • If the registered SIM is removed, swapped, or inactive, the app may stop working until re-verified.
    • Web-based services (such as WhatsApp Web or Telegram Web) must automatically log out at least once every six hours.
    • Users will need to re-authenticate periodically for web access.

    The six-hour auto-logout rule applies only to web sessions, not to the main mobile app, provided the SIM remains active in the device.

    Why Has This Rule Been Introduced?

    According to DoT, cybercriminals have been exploiting messaging platforms by operating accounts without the original SIM present. In some reported cases, fraudsters used such gaps to carry out phishing, impersonation, and financial scams.

    The SIM-binding requirement aims to:

    • Ensure every active account is linked to a verified SIM issued under KYC norms.
    • Improve traceability of digital communications.
    • Reduce misuse of telecom identifiers.
    • Strengthen fraud prevention measures.

    Officials state that this is part of a broader effort to curb online financial fraud and digital identity misuse.

    What Changes for Users?

    From March 1 onward:

    • Messaging apps must verify that the registered SIM is physically present in the primary device.
    • Web and desktop sessions will auto-logout at least every six hours.
    • Users who are travelling or roaming will not be affected, as long as the SIM remains active in the phone.

    Users who frequently switch devices or remove their SIM cards may experience additional verification prompts.

    Industry Response

    Reports indicate that some messaging platforms have already begun testing updates to comply with the directive. Beta versions of certain apps reportedly include prompts asking users to confirm that their registered SIM is inserted in the device.

    At the same time, an industry body representing major messaging platforms has challenged aspects of the rule in court, arguing that it may exceed regulatory authority. The government maintains that SIM-binding is necessary for cybersecurity and fraud prevention.

    What Users Should Do

    • Keep your registered SIM active in your primary device.
    • Avoid removing or swapping SIM cards unnecessarily.
    • Enable two-step verification where available.
    • Regularly review linked devices in messaging app settings.

    Related Articles

  • OWASP Mobile Top 10-2024: Critical Mobile App Security Risks Every Security Professional Should Know Mobile applications have become a major part of modern life....
  • Gujarat Fake Trading App Cyber Fraud Case: ₹49 Lakh Investment Scam Exposes Rising Digital Fraud Threats Introduction: Gujarat Fake Trading App Cyber Fraud Raises Major Security...
  • Telegram Mini Apps Crypto Scam: FEMITBOT Targets Users with Fake Dashboards A large-scale Telegram Mini Apps crypto scam 2026 campaign has...
  • WhatsApp Unencrypted Chat Storage Issue on macOS and iOS Raises Serious Cybersecurity Concerns Introduction: WhatsApp Unencrypted Chat Storage Explained The recently discovered WhatsApp...
  • QR Code Phishing Attacks : How Quishing Scams Are Targeting Mobile Users Introduction: QR Code Phishing Attacks Are Rapidly Increasing QR Code...
  • Share. Facebook Twitter LinkedIn Email Telegram

    latest news

    OpenAI AI Agents Breached Australian Government Portal in Wider Hacking Campaign

    September 28, 2026

    Viral “Rent A Garba Partner” Post Raises Cybersecurity Questions Amid Navratri Scam Warnings

    September 19, 2026

    Azure AI Foundry Vulnerability: CVSS 10.0

    September 18, 2026

    T-Mobile Rewards Phishing: Fake Expiry Scam Texts

    September 18, 2026

    Docker Sandboxes Vulnerabilities: Critical Flaws

    September 17, 2026

    HEAVYGRAM Malware: Telegram Surveillance Backdoor

    September 17, 2026

    SparroWocky Backdoor: FamousSparrow Targets Governments

    September 17, 2026

    CenterPoint Energy Data Breach: Customer Data Exposed

    September 16, 2026

    BambooToken Malware: Critical MQTT C2 Campaign

    September 16, 2026

    WordPress Plugin Attacks: Critical RCE Flaws Exposed

    September 16, 2026
    Recent Posts
    • OpenAI AI Agents Breached Australian Government Portal in Wider Hacking Campaign
    • Viral “Rent A Garba Partner” Post Raises Cybersecurity Questions Amid Navratri Scam Warnings
    • Azure AI Foundry Vulnerability: CVSS 10.0
    Top Posts

    OpenAI AI Agents Breached Australian Government Portal in Wider Hacking Campaign

    September 28, 2026

    Unauthorized Access Incident at Coupang Exposes Customer Data

    December 29, 2025

    Significant Data Breach at Korean Air Subcontractor Exposes Employee Records

    December 29, 2025
    About

    CyberNexora Blog provides trusted cybersecurity news, attack analysis, and security awareness updates. Our goal is to educate and inform readers about emerging cyber threats and best protection practices.

    Facebook X (Twitter) Instagram Pinterest LinkedIn
    Pages
    • Home
    • Cyber Incidents
    • laws & government
    • Penalties
    • Learn & Protect
    • Resources
    • Contact Us

    Get Cyber Security Alerts

    Thanks! Please check your email to confirm subscription.

    • About CyberNexora News
    • Privacy Policy
    © 2026 CyberNexora News. All Rights Reserved.

    Type above and press Enter to search. Press Esc to cancel.