Close Menu
    What's Hot

    TSMC Confirms Employee Data Leak After Hackers Claim 46,000 Records Stolen

    November 13, 2026

    Is Microsoft Outlook Hacked? Hackers Exploit Zero-Day to Steal Windows Authentication Hashes

    November 13, 2026

    PM Modi Warns of Cyber Terrorism: India’s Banking System Is a Target in Modern Economic Warfare

    November 12, 2026

    Nvidia CEO Chinese Spy Allegations: What We Know

    November 10, 2026

    Binance Hack: $6.3 Billion Crypto Theft Sparks Global Security Probe

    October 30, 2026
    Facebook X (Twitter) Instagram
    Friday, November 13
    CyberNexora News
    X (Twitter) Instagram LinkedIn
    • Home
    • Cyber Incidents
    • laws & government
    • Penalties
    • Learn & Protect
    • Resources
    • Contact Us
    Get Cyber Alerts
    CyberNexora News
    Home»Cyber Incidents»n8n Supply Chain Attack Uses Fake Community Nodes to Steal OAuth Credentials

    n8n Supply Chain Attack Uses Fake Community Nodes to Steal OAuth Credentials

    Malicious npm Packages Target n8n Automation Platform in Supply Chain Attack
    Zeel_CyberexpertBy Zeel_CyberexpertJanuary 13, 2026Updated:March 4, 20262 Mins Read
    Facebook Twitter LinkedIn Email Telegram

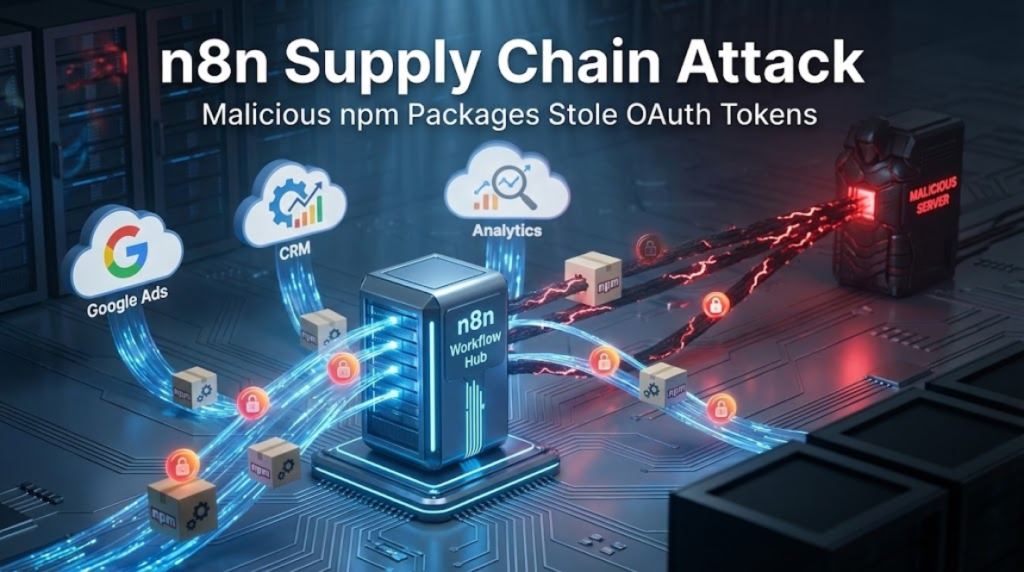
    Security researchers have identified a new supply chain attack targeting the n8n workflow automation platform, where attackers uploaded multiple malicious packages to the npm registry disguised as legitimate community nodes.

    These packages were crafted to resemble official integrations, including connectors for Google Ads and performance monitoring services. Once installed, they presented standard configuration interfaces, encouraging users to authorize external accounts. The provided OAuth credentials were then covertly extracted and transmitted to attacker-controlled infrastructure.
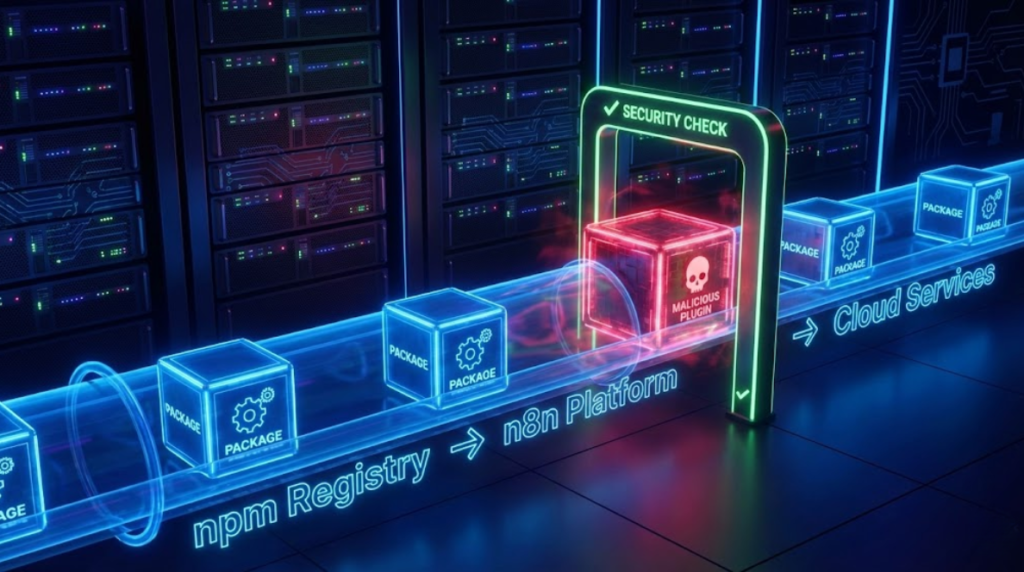
    One of the malicious packages imitated a Google Ads connector and prompted users to link their advertising account through what appeared to be a genuine authorization form. Behind the scenes, the credentials were intercepted and forwarded to remote servers without the user’s knowledge.

    According to security researchers, this campaign represents a notable shift in supply chain attacks. Instead of focusing on developer workstations, the attackers targeted automation platforms that store and manage sensitive credentials for multiple services in one place.

    At least eight npm packages were confirmed to contain malicious functionality before being removed from the registry. Some of these packages had already accumulated thousands of downloads. Additional related packages published by the same authors remain available, and their behavior is still under investigation.

    Analysis revealed that after installation, the malicious node stored credentials normally within n8n’s credential system. During workflow execution, the node accessed and decrypted the stored tokens using the platform’s internal mechanisms and then exfiltrated the data to external endpoints controlled by the attackers.
    This is the first publicly documented case of a supply chain attack explicitly focused on the n8n ecosystem. The incident demonstrates how trust in community-contributed automation components can be exploited to gain unauthorized access to business integrations and cloud services.

    Researchers also noted that n8n community nodes operate with the same privileges as the core platform. This allows a malicious node to access environment variables, read and write files, perform outbound network communication, and interact with decrypted credentials during execution, making detection difficult.

    The campaign is believed to be ongoing, as new versions of some packages were published shortly before the discovery was made public.

    Related Articles

  • Miasma Malware Hides in npm Packages to Steal Developer Secrets Introduction: Miasma Malware npm Packages — Why It Matters The...
  • Mini Shai-Hulud npm Supply Chain Attack Compromises AntV Packages and Developer Ecosystems Introduction: Mini Shai-Hulud Supply Chain Attack Expands Across npm Ecosystem...
  • Grafana GitHub Breach 2026: TanStack npm Supply Chain Attack Exposes Developer Infrastructure Risks Introduction: Grafana GitHub Breach Linked to TanStack npm Supply Chain...
  • VS Code Infostealer Attack: Critical npm Packages Hijacked VS Code Infostealer Attack — Why It Matters A newly...
  • Foxconn Ransomware Attack: 8TB Data Theft Claims Raise Major Supply Chain Security Concerns Introduction: Foxconn Cyberattack Creates Global Cybersecurity Concerns Foxconn Ransomware Attack...
  • Share. Facebook Twitter LinkedIn Email Telegram

    latest news

    TSMC Confirms Employee Data Leak After Hackers Claim 46,000 Records Stolen

    November 13, 2026

    Is Microsoft Outlook Hacked? Hackers Exploit Zero-Day to Steal Windows Authentication Hashes

    November 13, 2026

    PM Modi Warns of Cyber Terrorism: India’s Banking System Is a Target in Modern Economic Warfare

    November 12, 2026

    Nvidia CEO Chinese Spy Allegations: What We Know

    November 10, 2026

    Binance Hack: $6.3 Billion Crypto Theft Sparks Global Security Probe

    October 30, 2026

    Black October 2026: The Global Cybersecurity Wake-Up Call

    October 24, 2026

    VAPT Services in 2026: Why Vulnerability Assessment and Penetration Testing Are Essential for Cybersecurity

    October 22, 2026

    SBI Data Breach: 3.75 Lakh Dark Web Records Reviewed

    October 21, 2026

    AI Reverse Engineering Goes Viral as Adobe and Microsoft Face New Software Competition

    October 19, 2026

    Denmark Data Breach: 8.8 Million Records Accessed

    October 17, 2026
    Recent Posts
    • TSMC Confirms Employee Data Leak After Hackers Claim 46,000 Records Stolen
    • Is Microsoft Outlook Hacked? Hackers Exploit Zero-Day to Steal Windows Authentication Hashes
    • PM Modi Warns of Cyber Terrorism: India’s Banking System Is a Target in Modern Economic Warfare
    Top Posts

    Unauthorized Access Incident at Coupang Exposes Customer Data

    December 29, 2025

    TSMC Confirms Employee Data Leak After Hackers Claim 46,000 Records Stolen

    November 13, 2026

    Significant Data Breach at Korean Air Subcontractor Exposes Employee Records

    December 29, 2025
    About

    CyberNexora Blog provides trusted cybersecurity news, attack analysis, and security awareness updates. Our goal is to educate and inform readers about emerging cyber threats and best protection practices.

    Facebook X (Twitter) Instagram Pinterest LinkedIn
    Pages
    • Home
    • Cyber Incidents
    • laws & government
    • Penalties
    • Learn & Protect
    • Resources
    • Contact Us

    Get Cyber Security Alerts

    Thanks! Please check your email to confirm subscription.

    • About CyberNexora News
    • Privacy Policy
    © 2026 CyberNexora News. All Rights Reserved.

    Type above and press Enter to search. Press Esc to cancel.